How Does A Cryptographic Primitive Work?
Simply as achecksum or error-detecting code exposes bit errors launched bynoisy links or scratched disks, a cryptographic hash is designed toexpose deliberate corruption of messages by an adversary. The value https://www.cacainadjourney.com/2011/07/finding-right-security-system.html itoutputs is identified as a message digest and, like an ordinary checksum,is appended to the message. All the message digests produced by agiven hash have the same variety of bits whatever the size ofthe original message.
2 Secret-key Ciphers
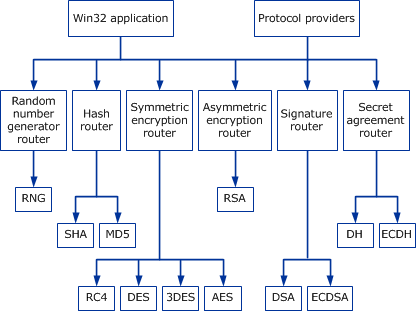
In many circumstances, the algorithm is a selectable parameter of those options, which suggests the general system does not turn into obsolete simply because considered one of its cryptography modules needs to be deprecated. As we noted in the previous chapter, the precept of open design has been proposed for security technologies since no much less than 1975. Cryptography has a much longer history than that, however, going back hundreds of years. Anybody can get the public key and then use it to encrypt a messagebefore sending it to the owner of the keys. Only the proprietor has theprivate key essential to decrypt such a message.

Digital Signatures
- To summarize, public-key ciphers may be used each for authentication and to assist confidential communications by encryption.
- Network safety tends to give consideration to the safety of information as it moves via the network—that is, information that is susceptible for under a short time frame.
- On receiving the message, the receiver computes a digest of the plaintext a part of the message and compares that to the decrypted message digest.
- Moreover, itcosts little to include the authenticator within the encryption, and itincreases security.
The 33-byte compressed illustration of the public secret is hashed with sha256 once. Traversing a Merkle tree includes ranging from the desired transaction and dealing up the tree to the basis hash. The path from the transaction to the Merkle tree root is called a Merkle proof. That would virtually be sufficient, however it seems that evidently the next candidate for collision finding is the widely-used SHA1 hash perform. Fortuitously NIST, the US organization liable for certifying cryptography, is actually two steps forward of this one. They’ve already begun a competition to choose a model new hash perform that may someday be designated SHA3.
11 Block Ciphers
Or moreaccurately, they might be effectively solved on quantum computersthat are much larger than any which have been built so far. Asprogress is made towards ever bigger quantum computer systems, measured bythe variety of quantum bits (qubits), there’s a realrisk that many current cryptographic algorithms will at some pointbecome breakable. Public-key ciphers are, sadly, a number of orders of magnitudeslower than secret-key ciphers. Consequently, secret-key ciphers areused for the vast majority of encryption, whereas public-key ciphers arereserved to be used in authentication and session key establishment.
Exactly howthis operation is used to provide authentication is the topic of alater chapter. Community security tends to concentrate on the safety of data as itmoves through the network—that is, knowledge that is susceptible for less than ashort period of time. In general, however, we must also contemplate thepossibility that knowledge might be captured for later analysis, or thatsome information might be saved in archives for tens of years. Thisargues much more strongly for a generously large key size to preparefor future computational advances. Nevertheless we do additionally want toconsider that larger keys are most likely to make encryption and decryptionslower.
Bech32 And Networkid Mapping
National Security Company (NSA) claims to have found them within the mid-1960s. The U.S. Nationwide Institute of Requirements and Know-how (NIST) has issued standards for a collection of secret-key ciphers. Data Encryption Commonplace (DES) was the first, and it survived for a number of decades earlier than being deprecated.
Bear In Mind that, inpractice, confidentiality is carried out utilizing secret-key ciphersbecause they are so much quicker than public-key ciphers. Furthermore, itcosts little to include the authenticator within the encryption, and itincreases security. A message authentication code may be created by encrypting the messagedigest with some key.
Like RSA, it relies on a mathematical drawback, the discrete logarithm downside, for which no efficient answer has been discovered, and requires keys of no less than 1024 bits. The fundamental requirement for an encryption algorithm is that it turns plaintext into ciphertext in such a means that solely the supposed recipient—the holder of the decryption key—can recuperate the plaintext. What this implies is that encrypted messages can’t be learn by people who don’t hold the key. When we say “cannot be read” we are going to make some assumptions about the computational capabilities and time out there to the attacker; extra on this in a moment.