How Will You Strengthen Saas Security? Csa
Every SaaS application has its own security settings, permission model, and sharing controls. A secure configuration in Salesforce looks very different from one in Slack or Google Workspace, making it tough to apply consistent safety insurance policies throughout dozens of platforms. As environments grow, configuration drift and inconsistent security https://lhcp2015.com/selecting-the-business-structure/ settings turn into more and more difficult to detect and remediate.
Zscaler’s Unified Platform
Users, contractors, companions, and service accounts continually achieve, change, and lose entry to SaaS applications. With Out steady monitoring and common entry evaluations, permissions shortly turn into outdated or excessive. The objective is to catch misconfigurations and over-permissive entry before they are exploited, and to take care of https://8wsm.com/technology/vpn-for-reddit-secure-private-and-unrestricted-access/ that state as new apps and integrations are added.
This apply carries severe cybersecurity dangers, since unvetted applications usually are not guaranteed to be properly secured, either in and of themselves or at the entry stage. Private e-mail domains and social media utilization are notable examples on this class. One Other finest apply is to coach and educate staff on protecting their gadgets and accounts from unauthorized access, in addition to guarantee secure knowledge sharing. For instance, you probably can define an inner coverage to recommend how delicate information can be transferred with most security. You ought to consult along with your IT team to arrange base-level person entry measures like multifactor authentication and role-based access management (RBAC).
Key Saas Security Posture Management Technologies
- For a broader view of how these layers interact, go to the Orca Safety Cloud Security Learning Hub.
- By consolidating instruments and enhancing visibility, organizations decrease operational costs whereas strengthening their overall safety posture.
- The customer is responsible for managing their information, user roles, and configurations.
- To make things worse, SaaS attackers are streamlining their tactics, strategies, and procedures (TTPs) to maneuver quickly from preliminary entry to information exfiltration, thereby skipping several phases in the MITRE ATT&CK framework.
SaaS compliance means ensuring your organization falls within a certified set of common standards and security policies—usually comprising how sensitive data is saved, shared, and used. Assembly these compliance standards shows your company’s willingness and competence to protect data and buyer privateness. Limit entry to your most sensitive information and belongings by solely giving trusted and bonafide customers entry to your corporate SaaS apps. The supplier manages the applying stack, when you remain liable for your users, information, integrations, and safety configurations. We all rely on SaaS apps to running our businesses, however are they secure enough to trust?
Achieve Full Visibility And Control
To maximize its effectiveness, an SSPM have to be integrated with specific business-critical SaaS applications and different SaaS security solutions to create a unified defense technique. Whereas SSPM helps enforce safety policies and remediate misconfigurations, it becomes even more highly effective when combined with SaaS discovery, identity safety, and automated remediation instruments. These integrations provide a extra full view of SaaS risk, guaranteeing organizations can establish safety gaps and take swift, automated action to mitigate them. Integrating SSPM with your safety tech stack enhances incident response, reduces guide workloads and strengthens compliance efforts, making it easier to secure the whole SaaS ecosystem whereas maintaining pace with business innovation. SaaS safety posture management (SSPM) repeatedly monitors your SaaS applications for misconfigurations, excessive permissions, and compliance gaps. It automates configuration evaluations across dozens or hundreds of applications, helping safety teams identify dangers that might be troublesome to detect manually.

Monitor Person Access And Knowledge Sharing
The reputation and speedy development of SaaS apps, along with their cloud-hosted mannequin, underscore the need for robust security. SaaS safety isn’t just a configuration problem anymore; it’s also an identity downside. As organizations adopt extra SaaS apps, typically without centralized oversight, the true danger isn’t simply misconfigured settings. It’s the sprawling ecosystem of accounts, identities, and access that accumulates over time, usually with out anyone noticing. Traditional instruments concentrate on isolated features of the issue, however securing SaaS in 2025 means understanding how users work together with apps, what information they’ll attain, and what happens when that entry outlives its objective. Meet with a SentinelOne professional to gauge your cloud safety posture across multi-cloud environments, uncover cloud assets, misconfigurations, secret scanning, and prioritize dangers with Verified Exploit Paths™.
Prime 10 Managed Soc Providers Providers For Companies In 2026
According to the 2025 safety priorities research by Foundry, 89% of surveyed companies are contemplating outsourcing some of their safety functions to an external vendor. Detection should produce clear documentation, and response actions must be traceable and accountable. Its worldwide delivery capabilities make it engaging for multinational organizations.
Fashionable SOC operations should help regulatory compliance across NIS2, DORA, CIRCIA, and SEC with documented incident response plans, automated detection, and fast reporting workflows. According to the Tines Voice of the SOC Analyst report (2025), 71% of SOC analysts report burnout and 64% are contemplating leaving their roles inside a 12 months. The ISC Cybersecurity Workforce Study discovered four.eight million unfilled cybersecurity roles globally, a 19% increase 12 months over year. Burnout mitigation strategies include automating SOC workflows to scale back repetitive triage, implementing rotating schedules, and investing in career development paths that give analysts a cause to stay. Some rely totally on SIEM and SOAR platforms, others emphasize XDR or EDR, and a growing number now incorporate AI-driven analysis alongside human analysts.
Anatomy Of A Contemporary Attack
- “AI-powered” now means radically various things relying on who you ask, and selections that once came right down to ingest cost now hinge on how nicely the platform understands the environment it protects.
- An intermediate SOC with defined processes runs roughly $2.5 million.
- Security Orchestration, Automation, and Response (SOAR) is a platform that helps security teams automate incident response by connecting instruments (SIEM, EDR/XDR, e-mail security, firewalls, IAM) into repeatable playbook workflows.
By providing centralized visibility and steady compliance assessment, CSPM enables SOC teams to safe cloud workloads at scale while responding sooner to evolving risks. Rapid7 InsightVM, Nessus, Tenable, and Qualys are main vulnerability administration instruments that present actionable vulnerability information, enabling teams to rapidly and successfully patch vulnerabilities. Efficient vulnerability administration reduces organizational danger, maintains compliance, and prevents attackers from exploiting recognized weaknesses. SIEM (Security Information and Event Management) collects and analyzes log knowledge to detect threats, whereas SOAR (Security Orchestration, Automation and Response) automates the response to these threats.
Selecting A Soar Platform: What Safety Teams Ought To Search For
For teams without Splunk experience, the operational overhead might outweigh the platform’s analytical energy. Organizations with excessive AI and automation adoption saved $1.9 million per breach and cut https://www.downloadwasp.com/71937/download-uniform-invoice-software-enterprise.html the breach lifecycle by 80 days (IBM 2025). According to the Vectra AI 2026 report, 76% of defenders say AI brokers now deal with greater than 10% of their workload.
Positioned as a SOAR replacement with considerably lower engineering upkeep prices as a outcome of AI-driven workflow generation. Less optimal for multi-cloud or vendor-diverse environments the place non-Microsoft log sources dominate. Enterprise deployments sometimes run $150+ per GB/day, with first-year complete prices ranging from $400,000–$800,000 together with infrastructure, implementation, and training.

A typical SIEM covers 6–8 ways, EDR covers 4–6, and even advanced XDR platforms reach solely 8–10. The board permitted $300K for “security modernization.” You consider 12 vendors, sit through 20 demos, and choose the Gartner Leader. Twelve months later, 40% of capabilities go unused, analysts nonetheless drown in alerts, and the CFO asks why breach danger has not decreased. This situation performs out at hundreds of mid-market corporations yearly, and it is virtually all the time brought on by the identical 5 procurement errors. Don’t overbuy complexity you can’t help or automation you won’t configure.
Q2 How Were These Soc Instruments Selected? (scoring Standards & Star Ratings)
If endpoints are your primary attack surface and you want best-in-class EDR with a clear upgrade path to XDR, Falcon is the natural place to begin. If 80%+ of your infrastructure runs on Microsoft, Sentinel gives you the most effective signal-to-noise ratio with minimal configuration. Log ingestion from Microsoft sources is both free or discounted, and the native Defender integration creates a detection-to-response pipeline that third-party SIEMs can’t replicate on the identical cost. The Vectra AI 2026 State of Risk Detection report, based mostly on 1,450 safety practitioners globally, discovered that whereas AI adoption is accelerating, 44% of defenders nonetheless feel they’re dropping floor.
Thehive + Cortex: Best Open-source Incident Response & Case Administration 📁
❌ Less mature than Splunk for customized analytics and less integrated than Sentinel for Microsoft environments. Be Taught tips on how to assess present state, sequence the work, build the business case, and measure progress. Organizations choose from in-house, outsourced, or hybrid SOC models primarily based on budget, staffing functionality, and the extent of control required. Nevertheless, inside assets alone are sometimes not enough to make SOC work correctly, so most firms usher in exterior specialists to help.
This is amongst the prime SOC as a Service corporations globally, with expertise in offering managed security companies and solutions for endpoint protection, phishing mitigation, cloud security, and community firewall home equipment. As a half of MDR options, the corporate provides prompt SOC providers, including 24/7 detection and response, expert-led threat hunting, incident response, and remediation consulting. The workflow begins with accumulating telemetry from networks, endpoints, cloud environments, id suppliers, SaaS applications, and security instruments.
How Does A Cryptographic Primitive Work?
Simply as achecksum or error-detecting code exposes bit errors launched bynoisy links or scratched disks, a cryptographic hash is designed toexpose deliberate corruption of messages by an adversary. The value https://www.cacainadjourney.com/2011/07/finding-right-security-system.html itoutputs is identified as a message digest and, like an ordinary checksum,is appended to the message. All the message digests produced by agiven hash have the same variety of bits whatever the size ofthe original message.
2 Secret-key Ciphers
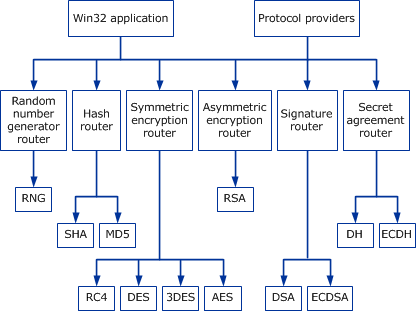
In many circumstances, the algorithm is a selectable parameter of those options, which suggests the general system does not turn into obsolete simply because considered one of its cryptography modules needs to be deprecated. As we noted in the previous chapter, the precept of open design has been proposed for security technologies since no much less than 1975. Cryptography has a much longer history than that, however, going back hundreds of years. Anybody can get the public key and then use it to encrypt a messagebefore sending it to the owner of the keys. Only the proprietor has theprivate key essential to decrypt such a message.

Digital Signatures
- To summarize, public-key ciphers may be used each for authentication and to assist confidential communications by encryption.
- Network safety tends to give consideration to the safety of information as it moves via the network—that is, information that is susceptible for under a short time frame.
- On receiving the message, the receiver computes a digest of the plaintext a part of the message and compares that to the decrypted message digest.
- Moreover, itcosts little to include the authenticator within the encryption, and itincreases security.
The 33-byte compressed illustration of the public secret is hashed with sha256 once. Traversing a Merkle tree includes ranging from the desired transaction and dealing up the tree to the basis hash. The path from the transaction to the Merkle tree root is called a Merkle proof. That would virtually be sufficient, however it seems that evidently the next candidate for collision finding is the widely-used SHA1 hash perform. Fortuitously NIST, the US organization liable for certifying cryptography, is actually two steps forward of this one. They’ve already begun a competition to choose a model new hash perform that may someday be designated SHA3.
11 Block Ciphers
Or moreaccurately, they might be effectively solved on quantum computersthat are much larger than any which have been built so far. Asprogress is made towards ever bigger quantum computer systems, measured bythe variety of quantum bits (qubits), there’s a realrisk that many current cryptographic algorithms will at some pointbecome breakable. Public-key ciphers are, sadly, a number of orders of magnitudeslower than secret-key ciphers. Consequently, secret-key ciphers areused for the vast majority of encryption, whereas public-key ciphers arereserved to be used in authentication and session key establishment.
Exactly howthis operation is used to provide authentication is the topic of alater chapter. Community security tends to concentrate on the safety of data as itmoves through the network—that is, knowledge that is susceptible for less than ashort period of time. In general, however, we must also contemplate thepossibility that knowledge might be captured for later analysis, or thatsome information might be saved in archives for tens of years. Thisargues much more strongly for a generously large key size to preparefor future computational advances. Nevertheless we do additionally want toconsider that larger keys are most likely to make encryption and decryptionslower.
Bech32 And Networkid Mapping
National Security Company (NSA) claims to have found them within the mid-1960s. The U.S. Nationwide Institute of Requirements and Know-how (NIST) has issued standards for a collection of secret-key ciphers. Data Encryption Commonplace (DES) was the first, and it survived for a number of decades earlier than being deprecated.
Bear In Mind that, inpractice, confidentiality is carried out utilizing secret-key ciphersbecause they are so much quicker than public-key ciphers. Furthermore, itcosts little to include the authenticator within the encryption, and itincreases security. A message authentication code may be created by encrypting the messagedigest with some key.
Like RSA, it relies on a mathematical drawback, the discrete logarithm downside, for which no efficient answer has been discovered, and requires keys of no less than 1024 bits. The fundamental requirement for an encryption algorithm is that it turns plaintext into ciphertext in such a means that solely the supposed recipient—the holder of the decryption key—can recuperate the plaintext. What this implies is that encrypted messages can’t be learn by people who don’t hold the key. When we say “cannot be read” we are going to make some assumptions about the computational capabilities and time out there to the attacker; extra on this in a moment.